Public Types |
Public Member Functions |
Static Public Member Functions |
Static Public Attributes |
Protected Member Functions |
Static Protected Member Functions |
Protected Attributes |
Private Member Functions |
Static Private Member Functions |
List of all members
xrpl::ConfidentialMPTMirrorUpdate Class Reference
Updates the encrypted mirror balances of a Confidential MPToken. More...
#include <ConfidentialMPTMirrorUpdate.h>
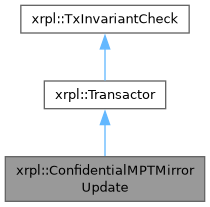
Inheritance diagram for xrpl::ConfidentialMPTMirrorUpdate:
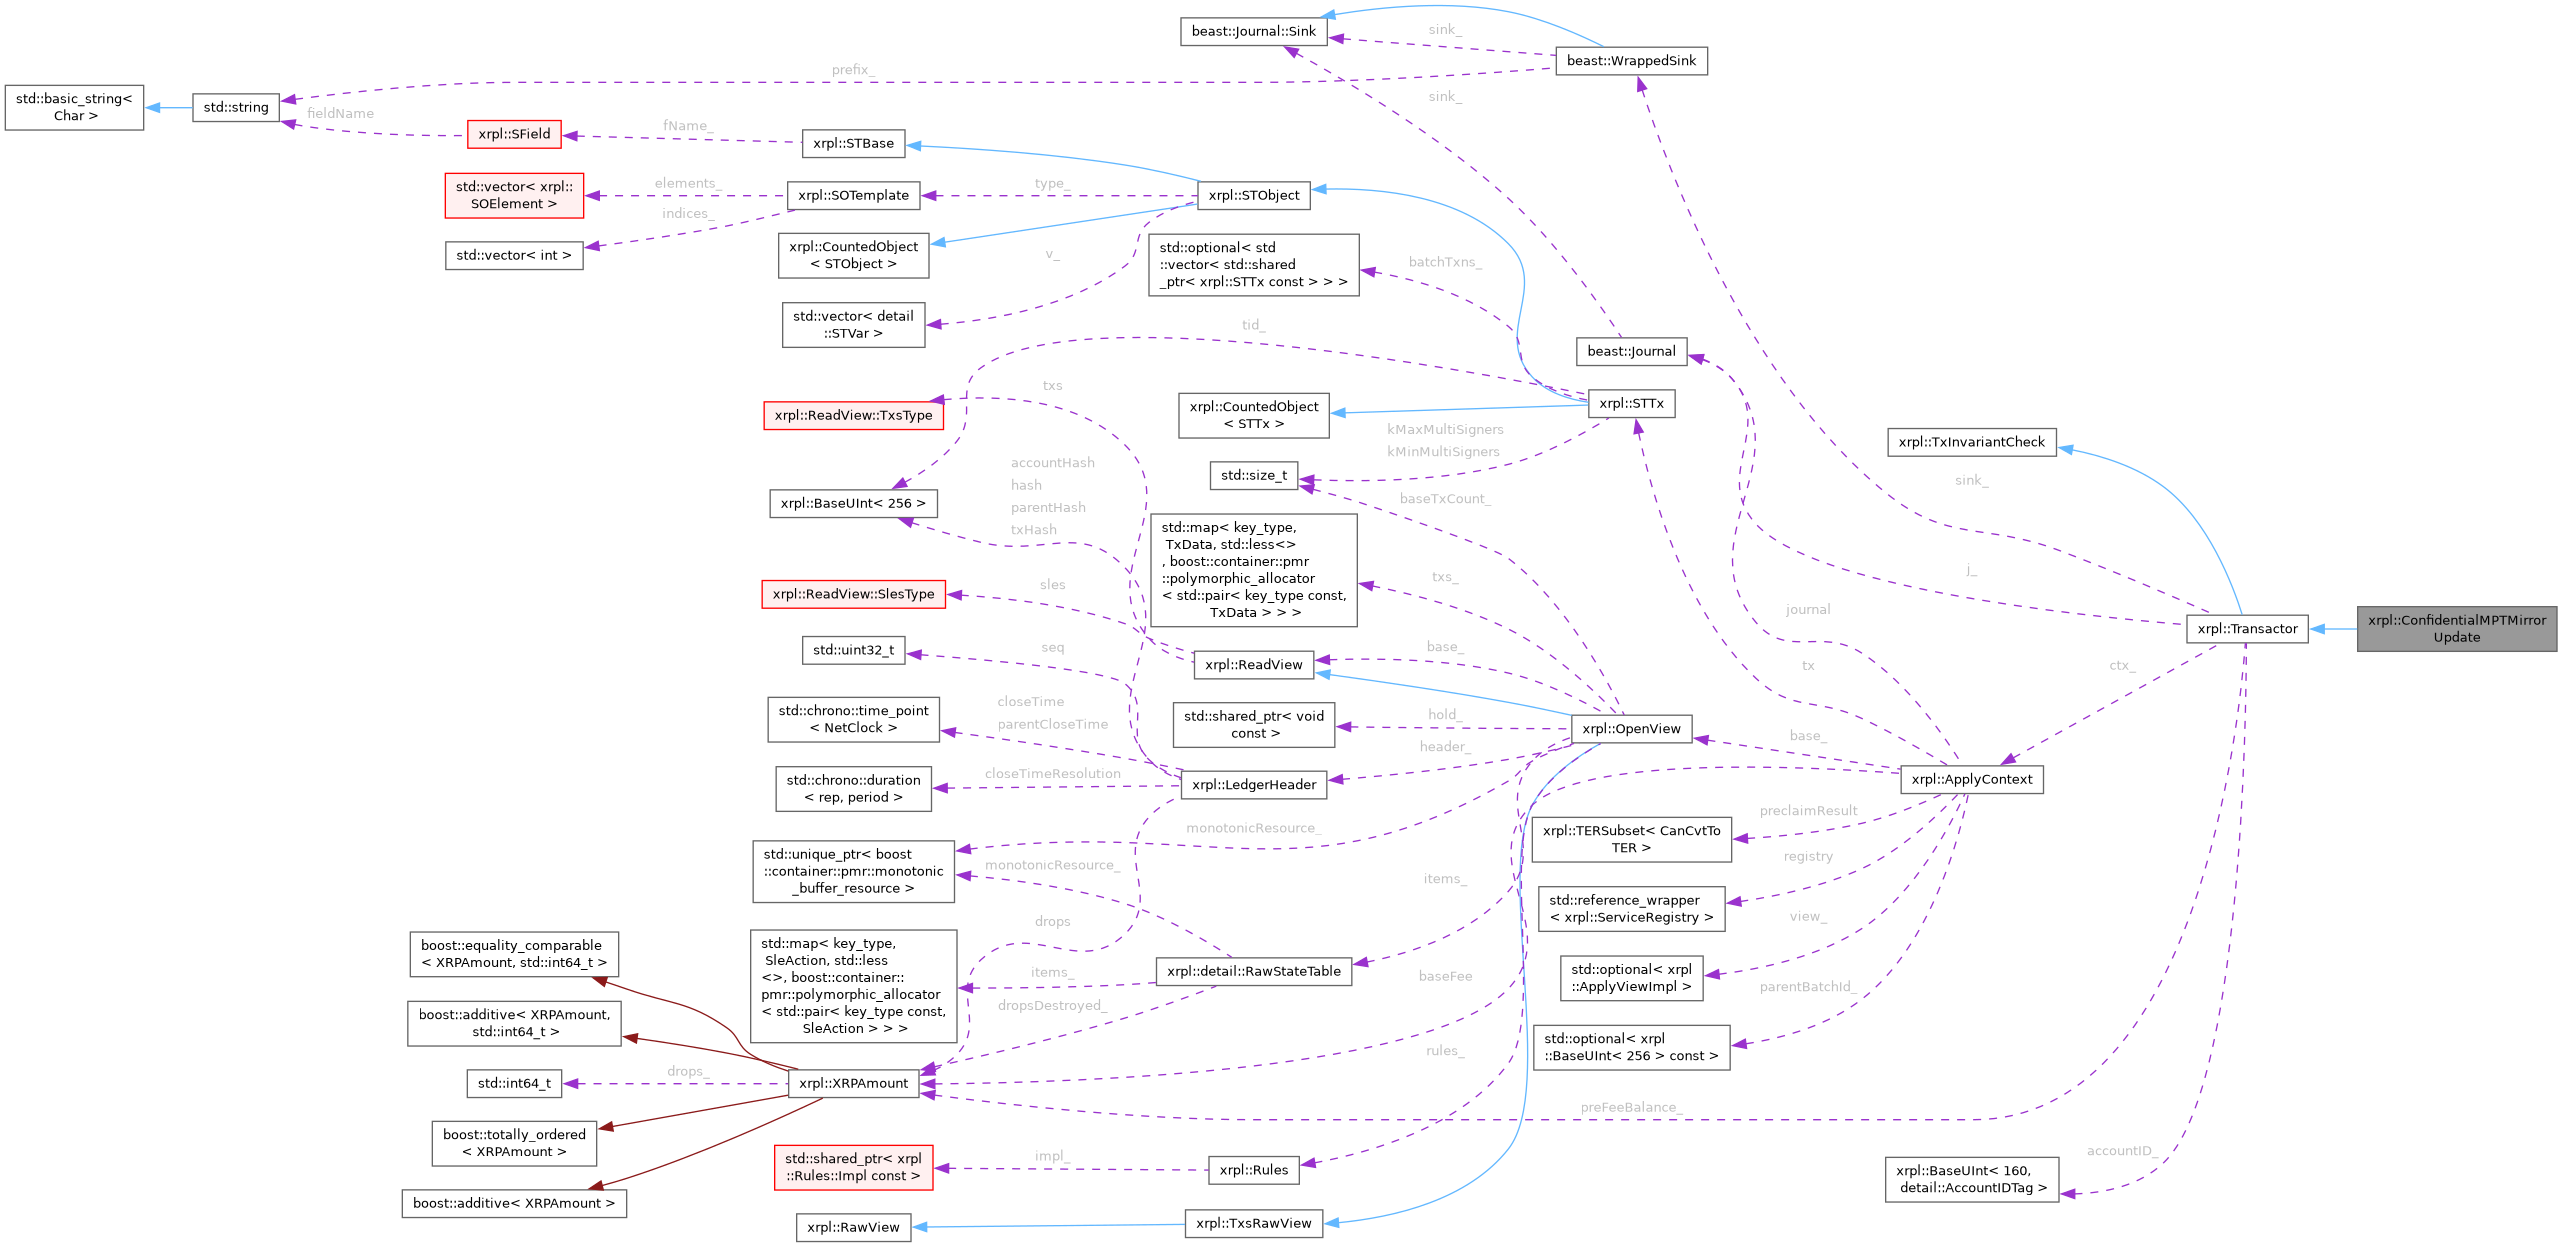
Collaboration diagram for xrpl::ConfidentialMPTMirrorUpdate:
Public Types | |
| enum class | ConsequencesFactoryType { Normal , Blocker , Custom } |
| enum class | InvariantScope { Full , ProtocolOnly } |
| Which invariant layers to check. More... | |
Public Member Functions | |
| ConfidentialMPTMirrorUpdate (ApplyContext &ctx) | |
| TER | doApply () override |
| void | visitInvariantEntry (bool isDelete, SLE::ConstRef before, SLE::ConstRef after) override |
| Inspect a single ledger entry modified by this transaction. | |
| bool | finalizeInvariants (STTx const &tx, TER result, XRPAmount fee, ReadView const &view, beast::Journal const &j) override |
| Check transaction-specific post-conditions after all entries have been visited. | |
| ApplyResult | operator() () |
| Process the transaction. | |
| ApplyView & | view () |
| ApplyView const & | view () const |
| TER | checkInvariants (TER result, XRPAmount fee, InvariantScope scope) |
| Check all invariants for the current transaction. | |
Static Public Member Functions | |
| static bool | checkExtraFeatures (PreflightContext const &ctx) |
| static NotTEC | preflight (PreflightContext const &ctx) |
| static XRPAmount | calculateBaseFee (ReadView const &view, STTx const &tx) |
| static TER | preclaim (PreclaimContext const &ctx) |
| static NotTEC | checkSeqProxy (ReadView const &view, STTx const &tx, beast::Journal j) |
| static NotTEC | checkPriorTxAndLastLedger (PreclaimContext const &ctx) |
| static TER | checkFee (PreclaimContext const &ctx, XRPAmount baseFee) |
| static NotTEC | checkSign (PreclaimContext const &ctx) |
| static XRPAmount | calculateBaseFee (ReadView const &view, STTx const &tx, std::uint32_t extraBaseFeeMultiplier) |
| static FeePayer | getFeePayer (ReadView const &view, STTx const &tx) |
| template<class T> | |
| static NotTEC | invokePreflight (PreflightContext const &ctx) |
| template<> | |
| NotTEC | invokePreflight (PreflightContext const &ctx) |
| template<> | |
| NotTEC | invokePreflight (PreflightContext const &ctx) |
| static NotTEC | checkGranularSemantics (ReadView const &view, STTx const &tx, std::unordered_set< GranularPermissionType > const &heldGranularPermissions) |
| This function can be overridden to introduce additional semantic constraints beyond the granular template validation for granular permissions. | |
| template<class T> | |
| static NotTEC | invokeCheckPermission (ReadView const &view, STTx const &tx) |
| Checks whether the transaction is authorized to be executed by the delegated account. | |
| static NotTEC | checkSponsor (ReadView const &view, STTx const &tx) |
| static TER | ticketDelete (ApplyView &view, AccountID const &account, UInt256 const &ticketIndex, beast::Journal j) |
Static Public Attributes | |
| static constexpr auto | kConsequencesFactory = ConsequencesFactoryType::Normal |
Protected Member Functions | |
| TER | apply () |
| virtual void | preCompute () |
Static Protected Member Functions | |
| static NotTEC | checkSign (ReadView const &view, ApplyFlags flags, std::optional< UInt256 const > const &parentBatchId, AccountID const &idAccount, STObject const &sigObject, beast::Journal const j, bool permitUncreatedAccount=false) |
| static XRPAmount | minimumFee (ServiceRegistry ®istry, XRPAmount baseFee, Fees const &fees, ApplyFlags flags) |
| Compute the minimum fee required to process a transaction with a given baseFee based on the current server load. | |
| static XRPAmount | calculateOwnerReserveFee (ReadView const &view, STTx const &tx) |
| static std::uint32_t | getFlagsMask (PreflightContext const &ctx) |
| static NotTEC | preflightSigValidated (PreflightContext const &ctx) |
| static bool | validDataLength (std::optional< Slice > const &slice, std::size_t maxLength) |
| template<class T> | |
| static bool | validNumericRange (std::optional< T > value, T max, T min=T{}) |
| template<class T, class Unit> | |
| static bool | validNumericRange (std::optional< T > value, unit::ValueUnit< Unit, T > max, unit::ValueUnit< Unit, T > min=unit::ValueUnit< Unit, T >{}) |
| template<class T> | |
| static bool | validNumericMinimum (std::optional< T > value, T min=T{}) |
| Minimum will usually be zero. | |
| template<class T, class Unit> | |
| static bool | validNumericMinimum (std::optional< T > value, unit::ValueUnit< Unit, T > min=unit::ValueUnit< Unit, T >{}) |
| Minimum will usually be zero. | |
| static NotTEC | checkSingleSign (ReadView const &view, AccountID const &idSigner, AccountID const &idAccount, SLE::const_pointer sleAccount, beast::Journal const j) |
| static NotTEC | checkMultiSign (ReadView const &view, ApplyFlags flags, AccountID const &id, STObject const &sigObject, beast::Journal const j) |
Protected Attributes | |
| ApplyContext & | ctx_ |
| beast::WrappedSink | sink_ |
| beast::Journal const | j_ |
| AccountID const | accountID_ |
| XRPAmount | preFeeBalance_ {} |
Private Member Functions | |
| std::pair< TER, XRPAmount > | reset (XRPAmount fee) |
| Reset the context, discarding any changes made and adjust the fee. | |
| TER | consumeSeqProxy (SLE::pointer const &sleAccount) |
| TER | payFee () |
| std::tuple< TER, XRPAmount, bool > | processPersistentChanges (TER result, XRPAmount fee) |
| void | trapTransaction (UInt256) const |
| void | visitEntry (bool isDelete, SLE::ConstRef before, SLE::ConstRef after) final |
| Bridges the two-phase TxInvariantCheck interface to this transactor's visitInvariantEntry/finalizeInvariants hooks. | |
| bool | finalize (STTx const &tx, TER result, XRPAmount fee, ReadView const &view, beast::Journal const &j) final |
| Called after all entries have been visited. | |
Static Private Member Functions | |
| static NotTEC | checkPermission (ReadView const &view, STTx const &tx, std::unordered_set< GranularPermissionType > &heldGranularPermissions) |
| static NotTEC | preflight1 (PreflightContext const &ctx, std::uint32_t flagMask) |
| Performs early sanity checks on the account and fee fields. | |
| static NotTEC | preflight2 (PreflightContext const &ctx) |
| Checks whether the signature appears valid. | |
| static NotTEC | preflightUniversal (PreflightContext const &ctx) |
| Universal validations. | |
Detailed Description
Updates the encrypted mirror balances of a Confidential MPToken.
This transaction updates a single holder's mirrored confidential balances (sfIssuerEncryptedBalance and/or sfAuditorEncryptedBalance) with the latest ElGamal public keys defined on the MPTokenIssuance.
It supports both issuer and holder self-migration modes, each mode supports multiple flows:
- Issuer mode: Submitted by the issuer.
- Issuer Key Rotation Migration: Re-encrypts the holder's sfIssuerEncryptedBalance under the issuer's new ElGamal public key.
- Auditor Key Rotation Migration: Re-encrypts the holder's sfAuditorEncryptedBalance under the auditor's new ElGamal public key.
- Simultaneous Rotation Migration: Updates both the issuer and auditor encrypted balances in a single transaction to optimize network throughput.
- Auditor Late-Registration Migration: When the issuer ElGamal public key is already registered on the MPTokenIssuance object, the issuer can register an auditor key at a later time through MPTokenIssuanceSet. Then the issuer uses this flow to set the holder's initial sfAuditorEncryptedBalance on MPToken object.
- Holder self-migration mode: Submitted by the holder. The holder decrypts their own sfConfidentialBalanceSpending with holder's private key to recover the balance and re-encrypts it under the relevant new ElGamal public key(s). This mode is always available to the holder and is not conditioned on the issuer being unable to migrate them: the ledger cannot verify whether an issuer has really lost its private key. That loss is only the expected motivation, since an issuer that still holds its key can migrate holders itself in issuer mode.
- Note
- All holder migration flows strictly require the holder's sfConfidentialBalanceInbox to be canonically zero; the holder must run ConfidentialMPTMergeInbox first so the spending balance reflects the full balance.
- Holder Issuer-Mirror Migration: Re-encrypts the holder's sfIssuerEncryptedBalance under the issuer's new ElGamal public key.
- Holder Auditor-Mirror Migration: Re-encrypts the holder's sfAuditorEncryptedBalance under the auditor's new ElGamal public key, or sets it for the first time when the auditor key was late-registered. This is the holder-driven counterpart to flows 2 and 4, for when the issuer does not migrate the holder itself.
- Simultaneous Holder Self-Migration: Updates both the issuer and auditor encrypted balances in a single transaction (both keys have rotated).
Definition at line 62 of file tx/transactors/token/ConfidentialMPTMirrorUpdate.h.
Member Enumeration Documentation
◆ ConsequencesFactoryType
|
stronginherited |
| Enumerator | |
|---|---|
| Normal | |
| Blocker | |
| Custom | |
Definition at line 175 of file Transactor.h.
◆ InvariantScope
|
stronginherited |
Which invariant layers to check.
Full runs the protocol invariants plus the transaction-specific check. This is always the scope of the initial pass, even when the tentative TER is a tec: a bug or exploit could still mutate ledger state, so transaction-specific invariants must run for failed transactions too.
ProtocolOnly runs only the protocol invariants and is used exclusively for the second invariant pass that follows a fee-claim reset — specifically, the reset that Transactor::operator() performs when the initial invariant pass returns tecINVARIANT_FAILED, rolling the transaction's effects back to a fee-claim-only state. In that reduced state the transaction-specific post-conditions no longer apply, but the protocol invariants must still hold against the fee claim itself. ProtocolOnly is not intended for other context discards (e.g. the reset used to handle tecOVERSIZE/tecKILLED/etc. in processPersistentChanges, or the ctx_.discard() done under TapFailHard); those paths do not re-run invariants at all.
| Enumerator | |
|---|---|
| Full | |
| ProtocolOnly | |
Definition at line 217 of file Transactor.h.
Constructor & Destructor Documentation
◆ ConfidentialMPTMirrorUpdate()
|
explicit |
Definition at line 67 of file tx/transactors/token/ConfidentialMPTMirrorUpdate.h.
Member Function Documentation
◆ checkExtraFeatures()
|
static |
Definition at line 23 of file ConfidentialMPTMirrorUpdate.cpp.
◆ preflight()
|
static |
Definition at line 30 of file ConfidentialMPTMirrorUpdate.cpp.
◆ calculateBaseFee() [1/2]
|
static |
Definition at line 86 of file ConfidentialMPTMirrorUpdate.cpp.
◆ preclaim()
|
static |
Definition at line 92 of file ConfidentialMPTMirrorUpdate.cpp.
◆ doApply()
|
overridevirtual |
Implements xrpl::Transactor.
Definition at line 208 of file ConfidentialMPTMirrorUpdate.cpp.
◆ visitInvariantEntry()
|
overridevirtual |
Inspect a single ledger entry modified by this transaction.
Called once for every SLE created, modified, or deleted by the transaction, before finalizeInvariants. Implementations should accumulate whatever state they need to verify transaction-specific post-conditions.
- Parameters
-
isDelete true if the entry was erased from the ledger. before the entry's state before the transaction (nullptr for newly created entries). after the entry's state as supplied by the apply logic for this transaction. For deletions, this is the SLE being erased and is not guaranteed to be null; callers must use isDelete rather than after == nullptr to detect deletions.
Implements xrpl::Transactor.
Definition at line 258 of file ConfidentialMPTMirrorUpdate.cpp.
◆ finalizeInvariants()
|
nodiscardoverridevirtual |
Check transaction-specific post-conditions after all entries have been visited.
Called once after every modified ledger entry has been passed to visitInvariantEntry. Returns true if all transaction-specific invariants hold, or false to fail the transaction with tecINVARIANT_FAILED.
- Parameters
-
tx the transaction being applied. result the tentative TER result so far. fee the fee consumed by the transaction. view read-only view of the ledger after the transaction. j journal for logging invariant failures.
- Returns
- true if all invariants pass; false otherwise.
Implements xrpl::Transactor.
Definition at line 263 of file ConfidentialMPTMirrorUpdate.cpp.
◆ operator()()
|
inherited |
Process the transaction.
Definition at line 1553 of file Transactor.cpp.
◆ view() [1/2]
|
inherited |
Definition at line 184 of file Transactor.h.
◆ view() [2/2]
|
nodiscardinherited |
Definition at line 190 of file Transactor.h.
◆ checkInvariants()
|
nodiscardinherited |
Check all invariants for the current transaction.
Delegates to the free xrpl::checkInvariants runner. When scope is InvariantScope::Full, this transactor is passed so both layers share a single walk of the modified ledger entries. A failure in either layer fails the transaction the same way: tecINVARIANT_FAILED on the first pass, which the caller may respond to by rolling the transaction back to a fee-claim state and re-invoking this with InvariantScope::ProtocolOnly; a failure on that post-reset pass escalates to tefINVARIANT_FAILED.
- Parameters
-
result the tentative TER from transaction processing. fee the fee consumed by the transaction. scope which invariant layers to check.
- Returns
- the final TER after all invariant checks.
Definition at line 1543 of file Transactor.cpp.
◆ checkSeqProxy()
|
staticinherited |
Definition at line 699 of file Transactor.cpp.
◆ checkPriorTxAndLastLedger()
|
staticinherited |
Definition at line 764 of file Transactor.cpp.
◆ checkFee()
|
staticinherited |
Definition at line 517 of file Transactor.cpp.
◆ checkSign() [1/2]
|
staticinherited |
Definition at line 1011 of file Transactor.cpp.
◆ checkSign() [2/2]
|
staticprotectedinherited |
Definition at line 918 of file Transactor.cpp.
◆ calculateBaseFee() [2/2]
|
staticinherited |
Definition at line 477 of file Transactor.cpp.
◆ getFeePayer()
Definition at line 1381 of file Transactor.cpp.
◆ invokePreflight() [1/3]
template<class T>
|
staticinherited |
Definition at line 648 of file Transactor.h.
◆ invokePreflight() [2/3]
template<>
|
staticinherited |
◆ invokePreflight() [3/3]
template<>
|
staticinherited |
Definition at line 34 of file Change.cpp.
◆ checkGranularSemantics()
|
staticinherited |
This function can be overridden to introduce additional semantic constraints beyond the granular template validation for granular permissions.
It is called by the base invokeCheckPermission method only after the transaction has successfully passed checkGranularSandbox.
Definition at line 321 of file Transactor.h.
◆ invokeCheckPermission()
template<class T>
|
staticinherited |
Checks whether the transaction is authorized to be executed by the delegated account.
This function enforces the strict permission check hierarchy. It is explicitly designed NOT to be overridden. Derived transactors must instead implement checkGranularSemantics to add custom validation logic for granular permissions.
The evaluation proceeds as follows:
- If transaction-level permission is granted, the function immediately returns tesSUCCESS.
- If transaction-level permission is not granted, the function checks whether the transaction matches the granular permission template defined in permissions.macro. If it does, it then calls checkGranularSemantics to perform any additional, fine-grained validation.
Definition at line 344 of file Transactor.h.
◆ checkSponsor()
Definition at line 412 of file Transactor.cpp.
◆ ticketDelete()
|
staticinherited |
Definition at line 810 of file Transactor.cpp.
◆ apply()
|
protectedinherited |
Definition at line 882 of file Transactor.cpp.
◆ preCompute()
|
protectedvirtualinherited |
Reimplemented in xrpl::Change, and xrpl::SignerListSet.
Definition at line 876 of file Transactor.cpp.
◆ minimumFee()
|
staticprotectedinherited |
Compute the minimum fee required to process a transaction with a given baseFee based on the current server load.
- Parameters
-
registry The service registry. baseFee The base fee of a candidate transaction
- See also
- xrpl::calculateBaseFee
- Parameters
-
fees Fee settings from the current ledger flags Transaction processing fees
Definition at line 507 of file Transactor.cpp.
◆ calculateOwnerReserveFee()
|
staticprotectedinherited |
Definition at line 487 of file Transactor.cpp.
◆ getFlagsMask()
|
staticprotectedinherited |
Definition at line 370 of file Transactor.cpp.
◆ preflightSigValidated()
|
staticprotectedinherited |
Definition at line 376 of file Transactor.cpp.
◆ validDataLength()
|
staticprotectedinherited |
Definition at line 362 of file Transactor.cpp.
◆ validNumericRange() [1/2]
template<class T>
|
staticprotectedinherited |
Definition at line 677 of file Transactor.h.
◆ validNumericRange() [2/2]
template<class T, class Unit>
|
staticprotectedinherited |
Definition at line 686 of file Transactor.h.
◆ validNumericMinimum() [1/2]
template<class T>
|
staticprotectedinherited |
Minimum will usually be zero.
Definition at line 696 of file Transactor.h.
◆ validNumericMinimum() [2/2]
template<class T, class Unit>
|
staticprotectedinherited |
Minimum will usually be zero.
Definition at line 705 of file Transactor.h.
◆ checkSingleSign()
|
staticprotectedinherited |
Definition at line 1019 of file Transactor.cpp.
◆ checkMultiSign()
|
staticprotectedinherited |
Definition at line 1051 of file Transactor.cpp.
◆ checkPermission()
|
staticprivateinherited |
Definition at line 382 of file Transactor.cpp.
◆ reset()
Reset the context, discarding any changes made and adjust the fee.
- Parameters
-
fee The transaction fee to be charged.
- Returns
- A pair containing the transaction result and the actual fee charged.
Definition at line 1295 of file Transactor.cpp.
◆ consumeSeqProxy()
|
privateinherited |
Definition at line 792 of file Transactor.cpp.
◆ payFee()
|
privateinherited |
Definition at line 623 of file Transactor.cpp.
◆ processPersistentChanges()
|
privateinherited |
Definition at line 1431 of file Transactor.cpp.
◆ trapTransaction()
|
privateinherited |
Definition at line 1425 of file Transactor.cpp.
◆ preflight1()
|
staticprivateinherited |
Performs early sanity checks on the account and fee fields.
(And passes flagMask to preflight0)
Do not try to call preflight1 from preflight() in derived classes. See the description of invokePreflight for details.
Definition at line 232 of file Transactor.cpp.
◆ preflight2()
|
staticprivateinherited |
Checks whether the signature appears valid.
Do not try to call preflight2 from preflight() in derived classes. See the description of invokePreflight for details.
Definition at line 303 of file Transactor.cpp.
◆ preflightUniversal()
|
staticprivateinherited |
Universal validations.
-
Do not try to call preflightUniversal from preflight() in derived classes. See the description of invokePreflight for details.
Definition at line 343 of file Transactor.cpp.
◆ visitEntry()
|
finalprivatevirtualinherited |
Bridges the two-phase TxInvariantCheck interface to this transactor's visitInvariantEntry/finalizeInvariants hooks.
Declared private (rather than protected, like the hooks they forward to) so that neither this transactor nor any subclass can call them directly through a Transactor& — only through the TxInvariantCheck& that the free xrpl::checkInvariants runner holds, which is where the two-phase ordering is enforced.
Implements xrpl::TxInvariantCheck.
Definition at line 593 of file Transactor.h.
◆ finalize()
|
nodiscardfinalprivatevirtualinherited |
Called after all entries have been visited.
- Parameters
-
tx the transaction being applied. result the tentative TER result of the transaction. fee the fee consumed by the transaction. view read-only view of the ledger after the transaction. j journal for logging invariant failures.
- Returns
- true if all invariants hold; false to fail with tecINVARIANT_FAILED / tefINVARIANT_FAILED.
Implements xrpl::TxInvariantCheck.
Definition at line 599 of file Transactor.h.
Member Data Documentation
◆ kConsequencesFactory
|
staticconstexpr |
Definition at line 65 of file tx/transactors/token/ConfidentialMPTMirrorUpdate.h.
◆ ctx_
|
protectedinherited |
Definition at line 162 of file Transactor.h.
◆ sink_
|
protectedinherited |
Definition at line 163 of file Transactor.h.
◆ j_
|
protectedinherited |
Definition at line 164 of file Transactor.h.
◆ accountID_
|
protectedinherited |
Definition at line 166 of file Transactor.h.
◆ preFeeBalance_
|
protectedinherited |
Definition at line 167 of file Transactor.h.
Generated by
 1.17.0